
Systemic & Fourth-Party Risk
See the risk hidden behind your vendors.
Your vendors rely on their own providers. Cynapze maps those fourth parties, classifies what it finds, and shows where risk concentrates across your extended supply chain.
My Vendors
Sort by Score
A
88
Acme Marketing
acme-marketing.com
Manage
B
81
1001 Cloud
1001cloud.eu
C
75
A2B Logistics
a2b-logistics.com
All my Vendors
+3 pts (30d)
Meridian Capital Inc.
merdian-capital.com
A
89
My Company Risk
Where a direct-vendor view leaves you exposed
The providers behind your providers
A breach two layers down can reach you as easily as one at a direct vendor.
Shadow vendors nobody logged
Suppliers connect to your environment without ever being formally recorded.
Hidden concentration
Several of your vendors may depend on the same provider, a single point of failure you can't see.
A register built from memory
Manually maintained lists drift out of date the moment relationships change.
No early warning on shared risk
When a widely used provider is hit, most organizations find out last.
Fourth parties outside every framework
Sub-providers rarely appear in the registers regulators expect you to keep.
How Cynnapze solves Systemic & Fourth-Party Risk
Collective Intelligence
Build a live graph of your vendors and the providers they depend on.
See how vendors interconnect, so exposure two steps out becomes visible.
Surface concentration where several vendors rely on the same provider.
Extend the same view to your regulated register, fourth parties included.

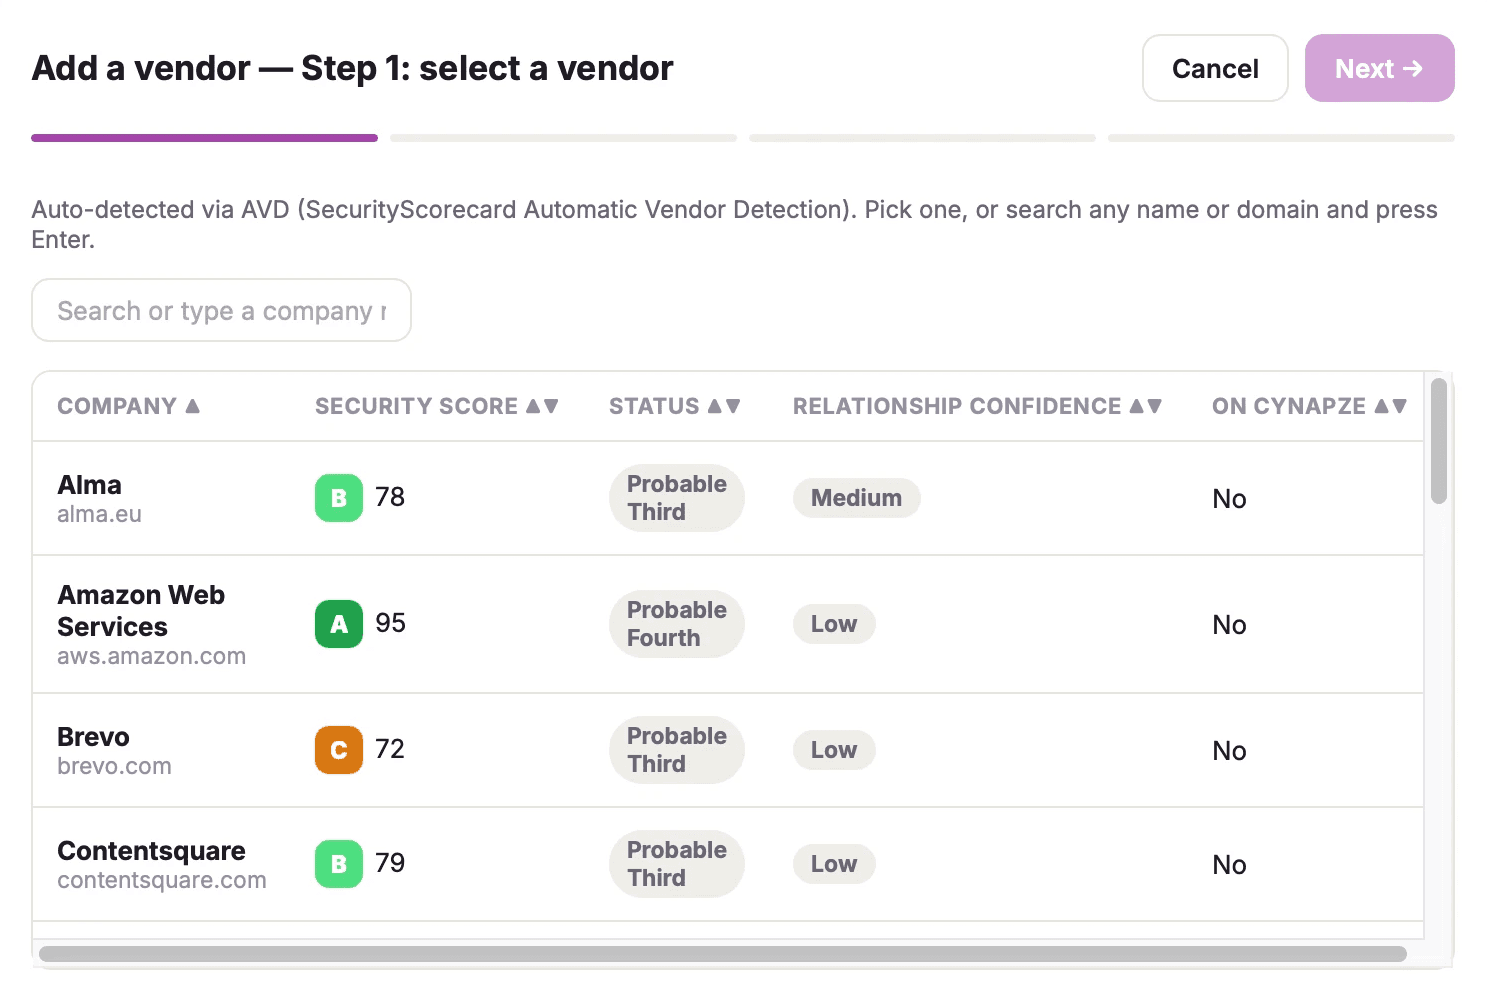
Discover fourth parties
Auto-detect vendors and sub-providers against a directory of 300,000 companies, not a blank list.
Classify each vendor from (AI-detected) probable fourth party, to monitored or managed vendor.
Close shadow IT blind spots without waiting for a manual declaration.
Keep the register current as relationships change, not once a year.
Get early warning
Get early warning when a shared provider is affected, across every vendor that relies on it.
Match emerging threats against the extended graph, not just direct vendors, to ultimately identify and rank systemic risk chains.
Leverage systemic risk chains to see at a glance which of your relationships a single incident touches.
Alert the owners of every affected vendor at the same time, and ultimately create a remediation plan across the board.

Act on concentration
Weigh each dependency by how many critical functions rely on it.
Prioritize the shared providers that would hurt most if they failed.
Turn a concentration finding into a remediation plan with an owner and a due date.
Report on systemic exposure for your board or your regulator.

One platform.
Explore more Cynapze solutions.
Cynapze brings every part of third-party risk into one platform. Explore the rest.

Collective Intelligence
A directory of 300,000 companies, and evidence shared once and reused across the network.
02.
Artificial Intelligence
03.
Continuous Vendor Monitoring
04.
Threat Intelligence
05.
Security Assessments
A network view, not a list of vendors
Cynapze shows the shared and fourth-party exposure a single-vendor view can never reveal, so concentration surfaces before it fails together.
Two steps out
Fourth parties in view, not just the vendors you contract with directly.
Concentration made visible
See where many vendors depend on the same provider.
Early warning on shared risk
When a shared provider is hit, everyone monitoring it is alerted at once.
Shadow vendors surfaced
Auto-detection finds the suppliers a manual list would miss.
Register that stays current
Your extended supply chain, kept up to date automatically.
Frequently
asked questions.
Can't find what you're looking for?
Reach out to our team at support@cynapze.com
General
Getting Started
Pricing
Regulations
Security & Privacy
What is Cynapze?
Cynapze is a third-party risk management platform. It helps organizations monitor, assess, and document the cybersecurity posture of their vendors and suppliers, all from one place.
Who is Cynapze built for?
Cynapze is built for organizations that need to manage vendor risk at scale, from security teams and risk officers to finance leaders who need visibility without becoming security experts.
How is Cynapze different from a spreadsheet or a manual review process?
Manual processes go stale the moment they're finished. Cynapze replaces static, point-in-time reviews with continuous monitoring, structured assessments, and a single record of every vendor's risk over time.
Do I need a security background to use Cynapze?
No. The platform is designed for both technical and non-technical roles, with role-based views that adapt to what each person on your team actually needs to see.
Can Cynapze scale with my vendor portfolio as it grows?
Yes. Whether you're managing a handful of vendors or several dozen, Cynapze is built to add vendors, assign criticality, and track risk without the process breaking down as your portfolio grows.

Vendor intelligence
for the threats that matter
With Cynapze, companies monitor their vendor ecosystem continuously,
meet regulatory requirements with confidence, and scale without losing visibility.

" height="24px" id="gjKBAxFFy" width="24px"/></svg>)
" height="20.571px" id="r9QMzLrOr" transform="translate(0 1.71)" width="24px"/></svg>)
Resources
Copyright ©2026 Cynpaze. All rights reserved.