
The TPRM platform powered by Collective & Artificial Intelligences
A platform where every vendor assessment becomes a signal, every signal feeds the network's collective intelligence, and AI turns it into remediation, resilience and continuous compliance.

Manual compliance carries a hidden cost.
Evidence gathering, spreadsheets and endless vendor back-and-forth. Your team spends more time producing reports than reducing risk and growing the business.
A single third-party breach can halt your operation.
Downtime, reputation damage, regulators notified and clients walking away. Not knowing your vendors' security posture is a risk you can't afford to take.
Cynapze provides continuous third-party risk management that keeps you compliant.
One platform to monitor, assess and manage your entire vendor ecosystem, without the operational overhead.
Our Standards
Built on data. Driven by results.
The numbers behind every vendor decision.
Speed
Under 1 day to deploy
Surface critical vendor risks instantly, and protect your supply chain from day one with zero onboarding friction.
Trust
200+ signals refreshed daily
Reliable signals, refreshed every day across all of your vendors.
Scale
300,000+ companies pre-scored
Zero cold start. Tap into an existing global network for instant risk visibility.
Outcome
100% of your risk addressed
Every issue assigned, tracked and closed. Nothing left undocumented.
Why Cynapze
One platform. Every vendor. Always under control.
Cynapze gives you the full picture of your vendor ecosystem, from initial scoring to compliance reporting, without the operational overhead.
Discover
1
Visualize
2
Monitor
3
Remediate
4
Comply
5
Discover
Vendor Risk Scoring
Know your vendors' security posture from day one.
Your vendors are already in our directory, scored and ready.
Automatic discovery extends visibility to third and fourth-party relationships.
Instant visibility on every vendor the moment you add them.
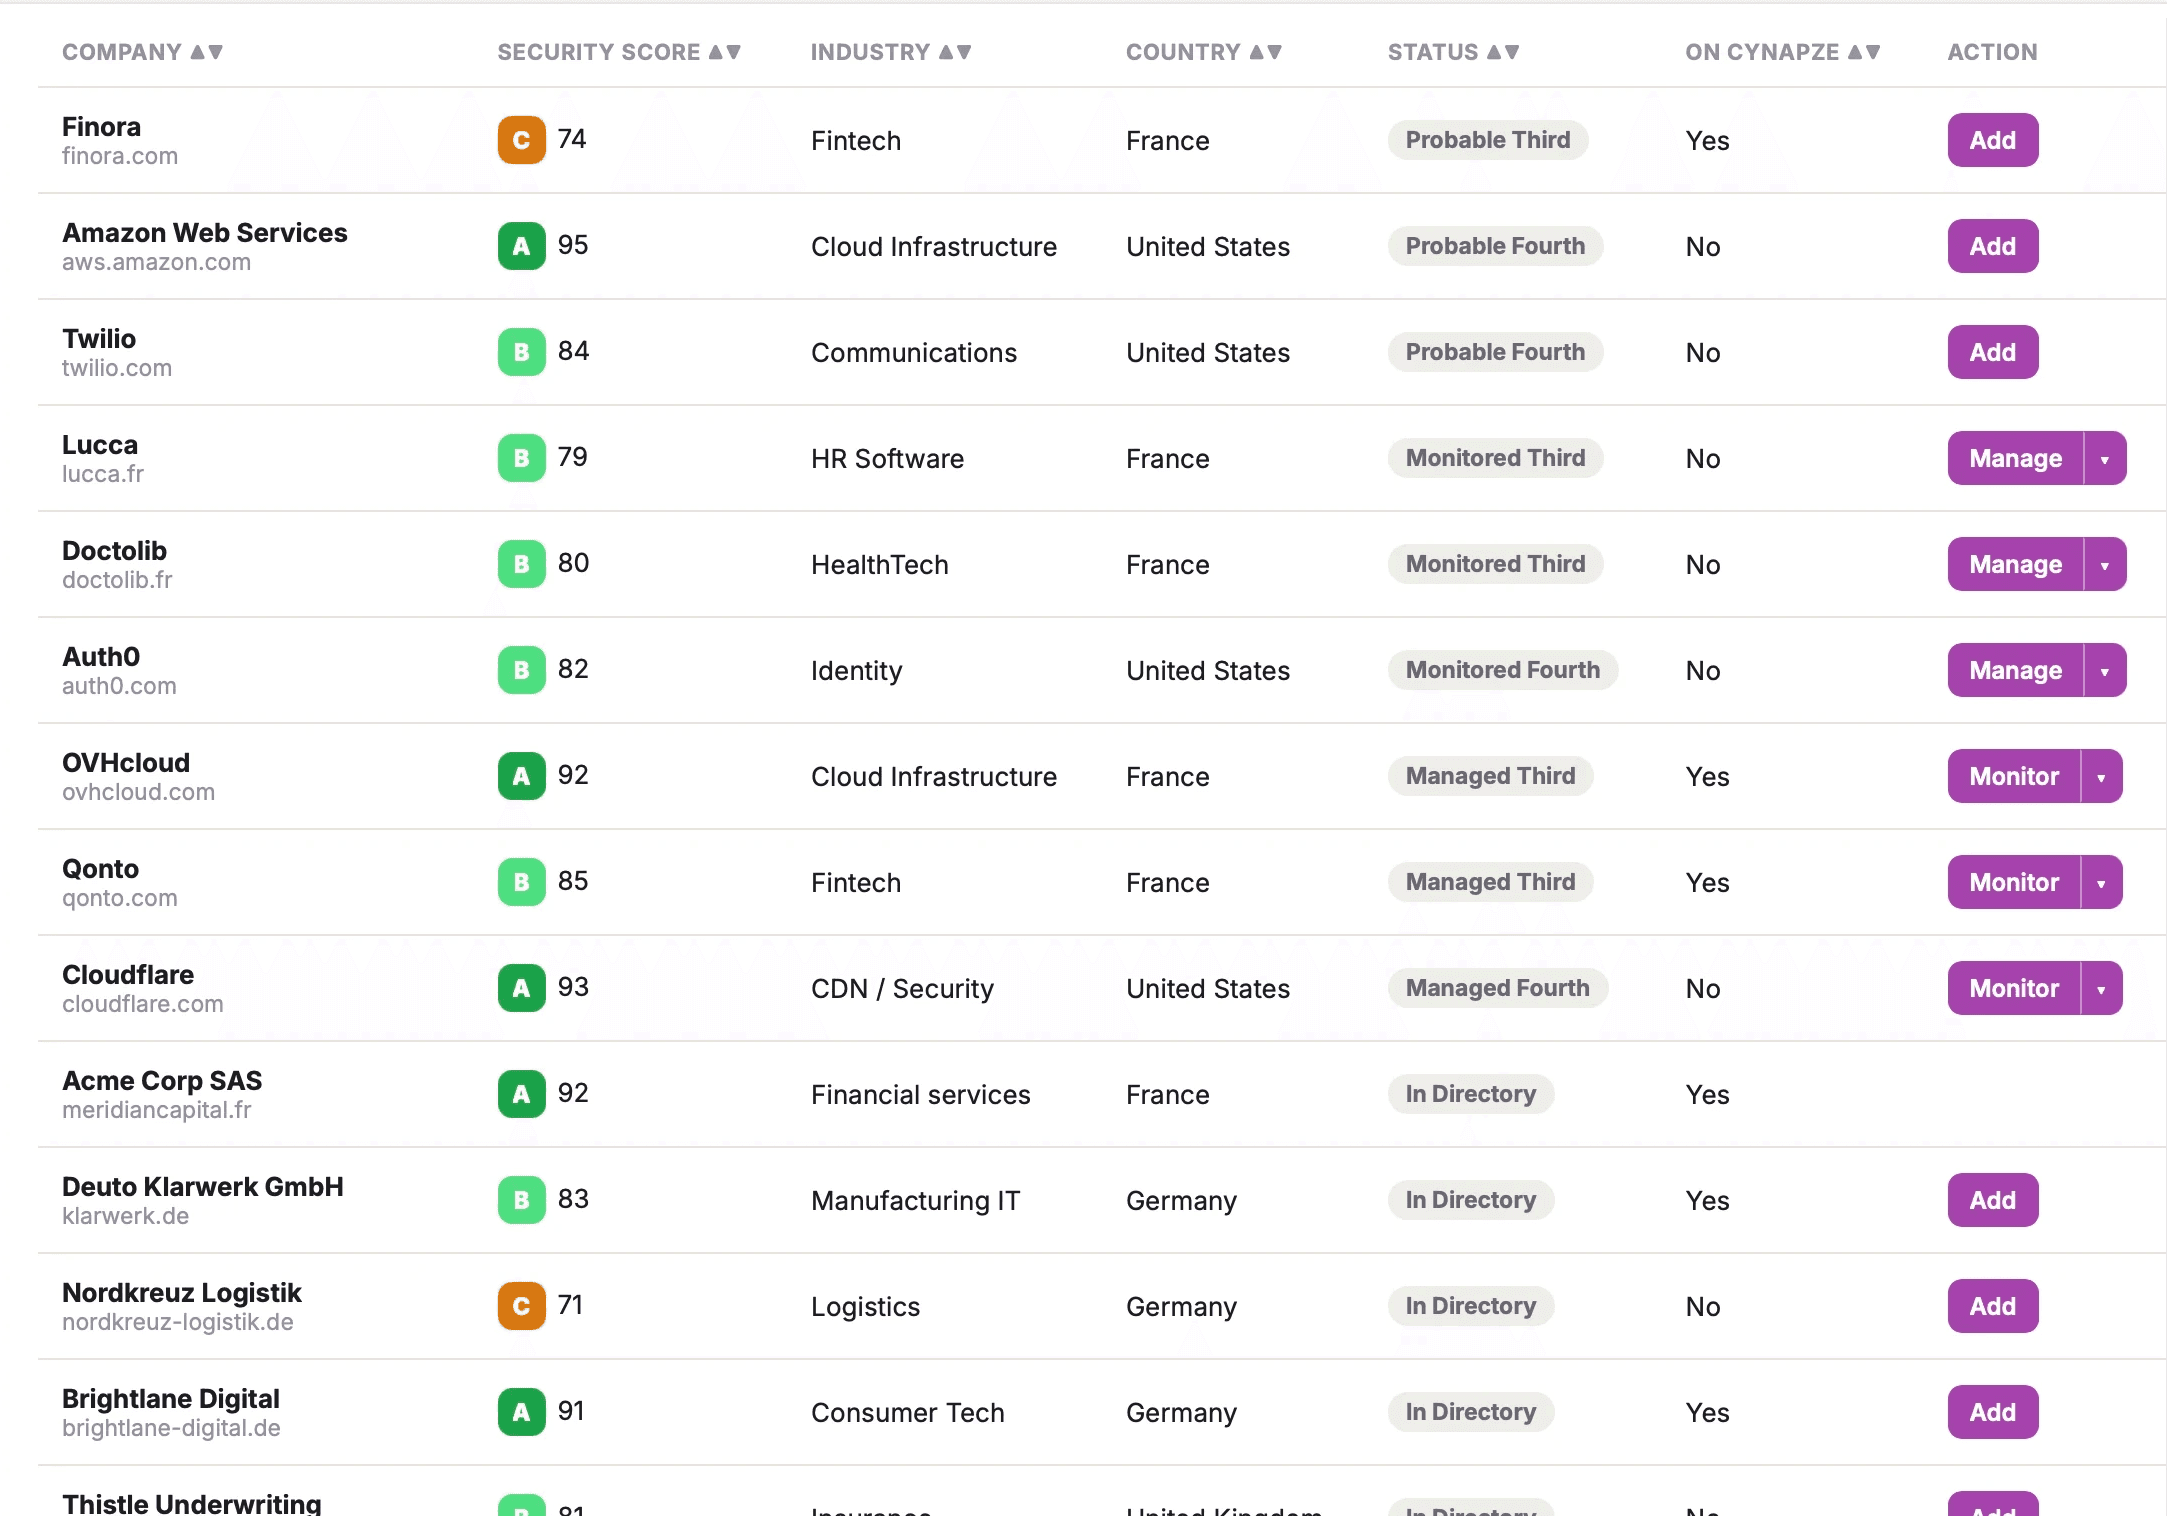
Collective Intelligence
A network sees what a single company cannot.
Your vendors are shared by thousands of organizations.
On Cynapze, a company brings its evidences, questionnaires and certifications once and shares them with everyone that relies on it. A third party is also a first party.
A directory of 300,000 companies, pre-scored and ready to monitor.
Evidences and Questionnaires shared once and reused. Muti party plans to scale and to accelerate remediation.
Your ecosystem raises your vendor risk intelligence up to identifying and remediating systemic risk chains.

Artificial Intelligence
AI does the busywork. You make the call.
Cynapze puts AI to work on the repetitive parts of vendor risk, and keeps every output a suggestion you review.
Discover hidden vendors
Auto-detect the third and fourth parties behind your suppliers, so nothing stays invisible.
Handle evidences and questionnaires
Read uploaded documents and draft questionnaire answers for you to review.
Prioritize what matters
AI Advices surface the few risks worth acting on first, across your portfolio.
Fix faster
Turn a finding into a suggested remediation plan, with an owner and steps proposed.
European sovereignty
Fully hosted in Europe, by design.
Your vendor data, assessments and evidences stay under European jurisdiction, with intelligence and AI that never leave the region.
European Cyber Threat Intelligence sources
Signals from ANSSI, ENISA and EU CSIRTs, with clear provenance.
Sovereign European cloud
Data and evidences kept under European jurisdiction.
Sovereign AI
Models run in Europe, never processed by a foreign one.
Tailored for every stage
From your first requirement to
an enterprise program.
Cynapze streamlines vendor risk monitoring, whether you are meeting your first compliance requirement
or running an enterprise-wide TPRM program.
SME's
First-time TPRM, without the complexity.
Get full visibility on your vendor ecosystem from day one
Meet DORA and NIS2 requirements without a dedicated security team
Up and running in hours, not months
Midmarket
Scale your vendor risk program without scaling your team.
Monitor dozens of third parties with continuous, automated scoring
Centralize remediation plans, questionnaires and evidence in one place
Demonstrate compliance to regulators and clients with confidence
Enterprise
Enterprise-grade TPRM, built for European sovereignty.
Manage dozens of critical vendors with full visibility on their security posture
Generate board-ready risk reports and respond to regulatory audits with confidence
Hosted in Europe, compliant with DORA and NIS2 from day one
Frequently
asked questions.
Can't find what you're looking for?
Reach out to our team at support@cynapze.com
General
Getting Started
Pricing
Regulations
Security & Privacy
What is Cynapze?
Cynapze is a third-party risk management platform. It helps organizations monitor, assess, and document the cybersecurity posture of their vendors and suppliers, all from one place.
Who is Cynapze built for?
Cynapze is built for organizations that need to manage vendor risk at scale, from security teams and risk officers to finance leaders who need visibility without becoming security experts.
How is Cynapze different from a spreadsheet or a manual review process?
Manual processes go stale the moment they're finished. Cynapze replaces static, point-in-time reviews with continuous monitoring, structured assessments, and a single record of every vendor's risk over time.
Do I need a security background to use Cynapze?
No. The platform is designed for both technical and non-technical roles, with role-based views that adapt to what each person on your team actually needs to see.
Can Cynapze scale with my vendor portfolio as it grows?
Yes. Whether you're managing a handful of vendors or several dozen, Cynapze is built to add vendors, assign criticality, and track risk without the process breaking down as your portfolio grows.

Vendor intelligence
for the threats that matter
With Cynapze, companies monitor their vendor ecosystem continuously,
meet regulatory requirements with confidence, and scale without losing visibility.

" height="24px" id="gjKBAxFFy" width="24px"/></svg>)
" height="20.571px" id="r9QMzLrOr" transform="translate(0 1.71)" width="24px"/></svg>)
Resources
Copyright ©2026 Cynpaze. All rights reserved.